
The 527-Day Hunt: How Investigators Tracked a Suspect Linked to the Pahalgam Attack

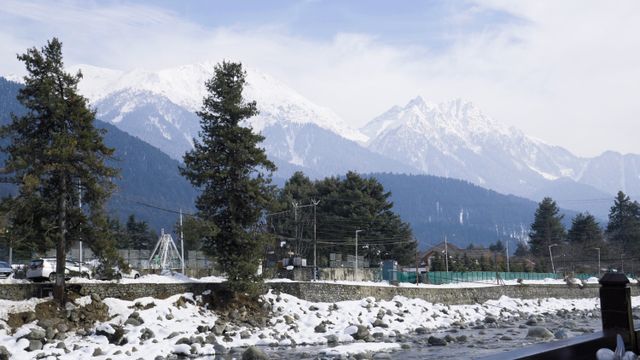

The investigation into the April 2025 Pahalgam terror attack became one of the most extensive counter-terrorism investigations in Jammu and Kashmir in recent years. The attack at Baisaran Valley near Pahalgam killed 26 people, including 25 tourists and a local pony operator, and triggered a large-scale effort to identify the attackers, reconstruct their movements and trace the wider network behind the assault.
More than a year after the attack, the investigation continued to develop through intelligence gathering, forensic examination, interrogation, digital evidence and operations against members of the broader militant network. One of the most closely watched figures was Mohammad Asif, also known as Hashim Moosa or Asif Fauji, a Pakistan-based Lashkar-e-Taiba commander whom security agencies linked to a wider group operating across Jammu and Kashmir. According to reporting by The Indian Express, his eventual death in an encounter in late September 2026 brought to an end what the newspaper described as a 527-day hunt for the last surviving member of the group associated with the Pahalgam attack.
The 527-day period refers to the time between the April 22, 2025 attack and the September 30, 2026 operation in which Asif was killed. The case illustrates how modern counter-terrorism investigations rarely depend on one decisive clue. Instead, they often develop through the gradual combination of witness accounts, digital records, technical intelligence, forensic material, intelligence inputs and information gathered during investigations into related attacks.
The story of the Pahalgam investigation therefore extends beyond the final encounter. It is also a story about how investigators reconstruct a network over time, connect apparently separate incidents and gradually narrow the field around individuals suspected of involvement.
The Pahalgam Attack and the Investigation That Followed
On April 22, 2025, armed terrorists attacked tourists in Baisaran Valley, a popular destination near Pahalgam in Jammu and Kashmir. Twenty-six people were killed in the assault. The incident immediately triggered a major investigation involving the National Investigation Agency and other security agencies.
The initial challenge was straightforward in principle but extremely difficult in practice: investigators had to establish who the attackers were, where they had come from, who had assisted them and how the attack had been planned.
The National Investigation Agency later said that two local men had been arrested for allegedly harbouring the attackers. In June 2025, the NIA stated that interrogation of the two accused had helped establish the identities of the three armed terrorists involved in the attack and that the agency was examining eyewitness accounts, video footage, technical evidence and sketches. The agency also cautioned at the time that some media reports about the identities of the attackers were speculative and that its evidence was still being analysed.
That distinction between an investigative lead and an established finding is important. Counter-terrorism cases often develop over months, and early information can change as evidence is corroborated.
From One Attack to a Larger Network
As investigators examined the Pahalgam attack, attention increasingly turned toward a wider militant network that had been active across the Pir Panjal region and the Kashmir Valley.
According to The Indian Express, Mohammad Asif, Hashim Moosa, Yasir and Sulaiman were associated with a four-member Lashkar-e-Taiba group that had operated in Jammu and Kashmir since around 2021. The newspaper reported that the group had been linked by security officials to several earlier attacks in Rajouri, Poonch, Kulgam and other areas.
The significance of reconstructing this network was that the Pahalgam attack did not appear in isolation. Investigators were examining a sequence of incidents and attempting to determine whether the same individuals, facilitators or organisational structures appeared repeatedly.
According to reporting, the group’s movements changed over time. In 2024, Junaid Ahmad Bhat was reported to have joined the group, after which members operated across a broader geographical area. Later that year, investigators connected members of the network to attacks in Gagangir and Gulmarg.
This wider timeline became important because every related incident could potentially provide additional evidence about the network.
The Gagangir and Gulmarg Attacks Added New Evidence
On October 20, 2024, an attack at a workers’ campsite near Gagangir in the Sonamarg area killed seven people, including a local doctor. According to The Indian Express, investigators later identified Junaid through CCTV footage connected with the incident. Four days later, another attack occurred in the Butapathri area of Gulmarg, where soldiers and porters were killed.
These incidents provided investigators with additional opportunities to study the network.
Security investigations often become stronger when evidence from separate cases begins to overlap. A person identified in one incident may appear in another investigation. A communication record may connect two locations. A witness statement may provide context for digital evidence. A recovered device may reveal information relevant to a different attack.
The Pahalgam investigation developed within this broader process of connecting separate pieces of evidence.
The First Major Breakthrough Came Before the Pahalgam Attack
One of the important developments in reconstructing the network came in December 2024, when Junaid was killed in an encounter in the Dachigam forests near Srinagar, according to The Indian Express. Another member of the group, Sulaiman, escaped from that encounter.
This pattern would later repeat itself. Members of the network were gradually eliminated or otherwise identified, while others remained difficult to locate.
The result was a prolonged investigation in which the security agencies were not simply looking for one person. They were attempting to understand an evolving network whose members had operated in difficult terrain and whose movements crossed different parts of Jammu and Kashmir.
That background helps explain why the hunt for Asif continued even after other members of the group had been killed.
Digital Evidence Became an Important Part of the Investigation
The Pahalgam investigation also demonstrated the growing importance of digital evidence in terrorism cases.
According to a report published by The Indian Express in June 2026, the NIA’s chargesheet included digital records recovered from mobile phones associated with terrorists killed after the Pahalgam attack. Investigators reportedly found map screenshots dated April 15 and 16, 2025 showing locations near Baisaran, suggesting that reconnaissance and planning activity had taken place approximately a week before the attack. The report also said investigators examined photographs, chats with a handler and information from specialised communication applications.
The importance of such evidence lies in its ability to reconstruct events after they have occurred.
Digital records can potentially establish sequences of activity, connections between individuals and relationships between locations. However, individual pieces of digital evidence generally need to be interpreted alongside other evidence rather than treated as self-explanatory proof.
In a complex investigation, the strength of a digital clue often comes from corroboration. A timestamp may become more meaningful when it aligns with a witness account. A photograph may acquire significance when investigators can establish who created it and when. A communication record may help explain a relationship that had already emerged from other evidence.
The GoPro Investigation Added Another Layer
Another notable strand of the investigation involved a GoPro camera recovered during the probe.
In March 2026, India Today reported that investigators had traced the device to a manufacturer and distributor in China. According to the report, the NIA told a special court that the camera could be relevant to reconstructing pre-attack reconnaissance, movements and preparations. The agency sought judicial assistance from Chinese authorities to establish more about the device’s chain of custody and eventual user.
The episode illustrates how modern terrorism investigations can cross international boundaries even when the attack itself occurs in a remote local setting.
A piece of equipment recovered during an investigation can potentially become part of a much larger evidentiary chain involving manufacturers, distributors, purchasers, users and communications. Establishing those links can require cooperation between countries and judicial systems.
The camera investigation therefore demonstrated another dimension of the Pahalgam case: the evidence did not necessarily remain confined to Jammu and Kashmir.
The Investigation Also Followed the Digital Propaganda Trail
Investigators examined not only physical and digital evidence connected to the attackers but also online claims surrounding the attack.
In June 2026, The New Indian Express reported that the NIA’s chargesheet said a claim of responsibility for the Pahalgam attack and a subsequent denial were traced to Pakistan-linked accounts associated with The Resistance Front. The first claim reportedly appeared on social media within hours of the attack before being withdrawn several days later.
The online dimension was significant because terrorism investigations increasingly involve two connected questions: what happened physically and how the event was represented digitally.
Online claims can provide investigative leads, but attribution requires technical examination. An account’s apparent location, affiliations or claims cannot automatically establish who physically carried out an attack.
For that reason, investigators generally have to compare digital material with physical evidence, witness testimony, communications records and other intelligence.
The Pahalgam Chargesheet Expanded the Picture
By December 2025, the NIA had filed a 1,597-page chargesheet naming seven accused, including the Pakistan-based LeT/TRF organisation and alleged Pakistani handler Sajid Jatt. The agency said the chargesheet detailed the alleged conspiracy, roles of accused persons and supporting evidence.
The chargesheet represented an important stage in the investigation because it moved the case from an initial search for attackers toward a broader reconstruction of alleged planning and facilitation.
Later developments continued to expand that picture. In 2026, the NIA named Pakistan-based LeT/TRF chief Hafiz Saeed in a supplementary chargesheet relating to the Pahalgam case.
These legal developments are separate from the field operations against individual terrorists. Together, however, they show that a terrorism investigation can proceed simultaneously along several tracks: identifying perpetrators, tracing facilitators, reconstructing the conspiracy and building evidence that can be presented in court.
Operation Mahadev and the Search for the Remaining Members
The investigation into the attackers eventually led to operations against members of the group in 2025.
According to The Tribune, the trail from the Pahalgam attack eventually led security forces toward the Dachigam forests, culminating in Operation Mahadev, during which the three terrorists identified as attackers were killed in July 2025.
The elimination of the three attackers did not end the broader investigation because security agencies were still pursuing members of the wider network.
This distinction is crucial. Identifying the individuals who physically carried out an attack is not necessarily the same as establishing the complete organisational structure behind it.
Investigators can continue examining facilitators, handlers, financiers, logistics networks and other people suspected of supporting a terrorist conspiracy.
Why Hashim Moosa Remained a Key Figure
According to The Indian Express, Asif remained the last surviving member of the four-member group that had been operating across Jammu and Kashmir. After other members were killed in separate encounters, the focus increasingly shifted toward locating him.
The newspaper reported that in September 2026, security forces received intelligence about the presence of Asif and another associate, Yasir, in the Ashdar Gali area. Yasir was killed during an encounter, while Asif escaped.
This was followed by further intelligence inputs later in September concerning suspicious movement near Yusmarg.
The eventual operation was therefore not presented as the result of one sudden discovery. Official accounts described it as the culmination of sustained intelligence collection and coordination.
Operation Sheruwali and the Final Operation
The Union government said that Asif was killed on September 30, 2026, during an intelligence-led joint operation in Budgam district. The Ministry of Home Affairs described the operation as part of a longer effort and said security forces had been pursuing him for an extended period. It also said a specific joint plan had been developed after technical and human intelligence indicated his movement and presence.
The government identified the operation as part of Operation Sheruwali, which it said had begun in May 2026.
The operation ended with Asif’s death and, according to the government, completed the neutralisation of the four-member LeT group that had been operating in Jammu and Kashmir since 2022 and had been associated by investigators with several attacks.
The term “neutralised” is used in official security communications to describe the killing of a militant during an operation. In a journalistic account, it is important to distinguish that official terminology from the broader legal process surrounding the alleged role of individuals in terrorism.
What the 527-Day Hunt Reveals About Modern Investigations
The 527-day period illustrates an important feature of modern counter-terrorism investigations: they are cumulative.
The investigation did not appear to depend on one dramatic clue. Instead, information accumulated across multiple incidents and evidence streams. Witness accounts, CCTV footage, digital records, communications, recovered devices, intelligence inputs and information from related investigations gradually contributed to a broader picture.
The investigation also demonstrates the importance of time. A suspect may remain unidentified or uncaptured even while investigators continue to build a profile around a network. Each subsequent incident can produce new evidence that changes how earlier events are understood.
The case further demonstrates the importance of distinguishing between the immediate perpetrators of an attack and the larger network that may support them.
The Role of Technology in Terror Investigations
Technology has become increasingly important in reconstructing complex criminal and terrorist cases.
Mobile devices can preserve timestamps, photographs and communications. Cameras can establish movements and identities. Online platforms can provide records of claims and communications. Digital forensic techniques can help investigators examine information that might otherwise remain difficult to interpret.
However, technology does not eliminate investigative uncertainty.
Digital information can be incomplete, misleading or difficult to attribute. Devices can change hands. Accounts can be operated by different people. Images can be copied. Metadata can require independent verification.
For this reason, the strongest investigations generally combine technical evidence with human intelligence and conventional investigative methods.
The Pahalgam case demonstrates precisely this combination, with official and media reports describing the use of eyewitness accounts, video evidence, technical information, digital records and intelligence inputs across different stages of the investigation.
The Legal Dimension Remains Separate From the Security Operation
Another important aspect of the case is the distinction between an encounter and a judicial determination.
Security agencies may identify an individual as a terrorist or suspect based on intelligence and investigative findings. A chargesheet represents the prosecution’s case and supporting evidence. A court, however, remains responsible for determining criminal liability in proceedings involving accused persons who are brought before it.
In the Pahalgam case, several accused and alleged conspirators have been named in NIA chargesheets, while other alleged perpetrators were killed during security operations.
This means that the investigative narrative and the judicial process are related but not identical. Evidence gathered by investigators must still meet applicable legal standards when presented in court.
A Long Investigation Rather Than a Single Breakthrough
The 527-day hunt for Hashim Moosa can therefore be understood as one chapter in a much longer investigation into the Pahalgam attack and the network associated with it.
The attack itself occurred on April 22, 2025. The investigation subsequently developed through arrests, interrogation, digital forensics, analysis of related attacks, examination of online activity and continuing intelligence operations. The NIA’s chargesheet and later supplementary filings expanded the alleged conspiracy under investigation, while security operations continued against members of the wider militant network.
The September 30, 2026 operation that killed Asif marked a significant endpoint in the pursuit of one of the remaining figures associated by security agencies with that network.
But the broader case continues to have a legal and investigative dimension beyond the death of an individual suspect. Establishing responsibility for an attack involves more than locating the people who carried it out. It requires reconstructing the chain of planning, facilitation, financing, communication and support, and presenting evidence in a form that can withstand judicial scrutiny.
Conclusion
The 527-day hunt for Mohammad Asif, also known as Hashim Moosa, illustrates how a major terrorism investigation can develop gradually over time. The Pahalgam attack of April 2025 generated an immediate search for the attackers, but the investigation soon expanded into a broader examination of the network operating across Jammu and Kashmir.
Investigators relied on multiple forms of evidence and intelligence. Official records describe the use of eyewitness accounts, video footage and technical evidence, while subsequent reporting detailed the examination of mobile phones, digital records, communications, online activity and recovered equipment.
The eventual killing of Hashim Moosa in an intelligence-led operation on September 30, 2026 came after other members of the group had been killed in separate encounters and after months of continuing efforts to locate the remaining suspect. The Ministry of Home Affairs described the operation as part of Operation Sheruwali and said it followed sustained intelligence gathering and coordination.
The case ultimately demonstrates that modern counter-terrorism investigations are built through accumulation. A witness statement can provide a lead, digital evidence can establish a timeline, forensic examination can connect objects to events, and intelligence can help investigators locate individuals. None of these elements necessarily tells the complete story by itself.
The Pahalgam investigation also underscores the importance of distinguishing investigative claims from judicial findings. As the case continues through legal processes, the evidence gathered by investigators will remain central to establishing responsibility and documenting the broader conspiracy.
The 527-day hunt may have ended with the final operation against one of the network’s remaining members, but the larger process of understanding, documenting and legally establishing what happened in Pahalgam extends well beyond the conclusion of a single manhunt.
Online Internship with Certificate
You may be interested
Why Tracking Satellites Has Become a Strategic Technology for Modern Nations
Anshika Jain - Oct 02, 2026Space has become an increasingly important part of modern infrastructure. Satellites support communications, navigation, weather forecasting, agriculture, disaster management, scientific research, financial services, television, internet connectivity and…
Can AI Help Cities Identify Pollution Sources Before They Become Public-Health Emergencies?
Anshika Jain - Oct 02, 2026Air pollution has traditionally been managed by measuring what is already happening. Monitoring stations record concentrations of pollutants, environmental agencies publish air-quality readings, and public authorities respond…
Why Food Hygiene Is Becoming a Major Student-Activism Issue
Anshika Jain - Oct 02, 2026Food is one of the most basic parts of campus life, yet it is also one of the areas where students can feel that they have the…
Most from this category
From Hostel Rules to Security: Women Students Demanding Participation in Decisions
Anshika Jain - Oct 02, 2026
Nirma University Women’s Safety Protest: Why Students Held a “Black Day” on Campus
Anshika Jain - Oct 02, 2026
When a Celebrity Becomes Part of a Regulatory Investigation: What Happens Next?
Anshika Jain - Oct 01, 2026
The Evidence Problem in High-Profile Crime Cases: Why Early Investigation Matters
Anshika Jain - Oct 01, 2026
From Hostel Rules to Security: Women Students Demanding Participation in Decisions
Anshika Jain - Oct 02, 2026Nirma University Women’s Safety Protest: Why Students Held a “Black Day” on Campus
Anshika Jain - Oct 02, 2026When a Celebrity Becomes Part of a Regulatory Investigation: What Happens Next?
Anshika Jain - Oct 01, 2026